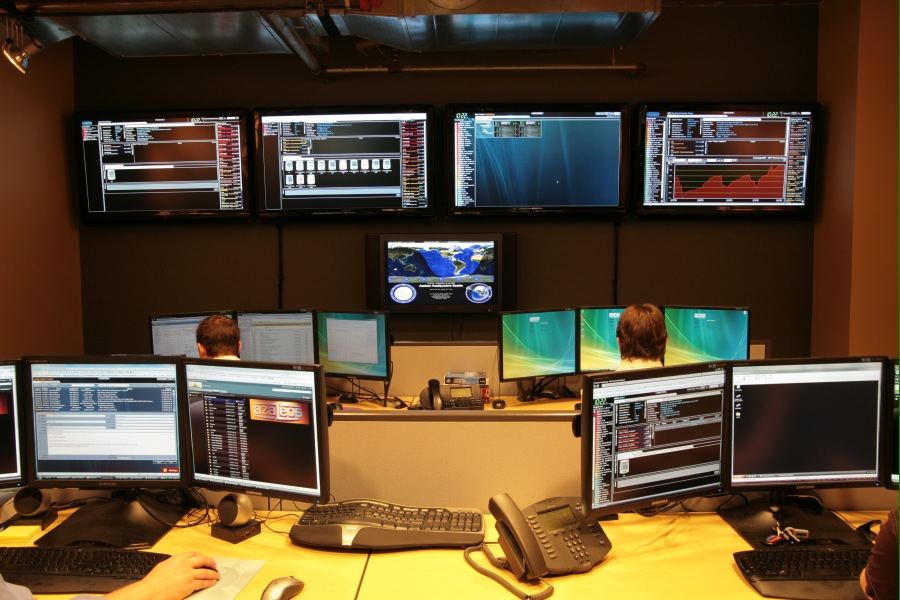

The worst moment to discover that nobody knows who may authorise shutting down a hospital network or a payment system is during a real ransomware attack. Organisations are therefore running simulated ransomware drills that test people and decisions, not just software. In a typical exercise, a scenario unfolds over hours: helpdesk calls about unreadable files, alerts from detection tools, a ransom note, then pressure from journalists and regulators as the fictional incident spreads. Participants from technology, legal, communications and senior management must coordinate under time pressure, deciding what to isolate, what to disclose and which services take priority for recovery. Facilitators deliberately inject complications, such as discovering that backups were also encrypted or that a key supplier is affected, because real incidents rarely follow the plan. The goal is not to catch individuals out but to find the seams between teams, the missing phone numbers, the unclear authorities and the assumptions that would slow a genuine response by hours when hours decide the damage.
What the Evidence Shows
Organisations that drill regularly report a consistent pattern: the technical steps of isolating systems and restoring data improve quickly, while communication decisions remain the hardest part. When to inform customers, staff and regulators, and what can honestly be said before facts are confirmed, requires judgement that only practice builds. Drills also reveal mundane weaknesses with outsized consequences, such as incident plans stored on the very network an attack would encrypt, or out-of-band contact lists that are months out of date. Mature programmes rotate scenarios across suppliers, cloud services and operational technology, and they track actions afterwards so identified fixes are completed rather than rediscovered at the next exercise. There is growing interest in sharing anonymised lessons between organisations in the same sector, since attackers reuse methods widely. A simulated attack costs a day of senior time, which can feel expensive until compared with the alternative. In a real incident, the organisations that cope best are usually those for whom the chaos already feels familiar. Reporting and analysis from sources such as MIT Technology Review track the same developments, and specialists following simulated ransomware drills testing coordinated response say the direction is now consistent across independent lines of evidence.
The Wider Context
The wider context is an industry learning to ship capability and restraint together. Products built around simulated ransomware drills testing coordinated response now launch with safety evaluations, usage data and rollback plans as standard, because enterprise buyers and regulators ask for them in the first meeting. Companies that treated those questions as friction are discovering they have become the purchase criteria.
What Happens Next
What happens next for simulated ransomware drills testing coordinated response depends less on another breakthrough than on the unglamorous work of reliability, pricing and support. The buyers evaluating it now are not enthusiasts; they are operators with budgets and auditors, and their checklists will decide the timeline. On the evidence of the current pilots, the technology has earned the right to be judged by them. You can follow related developments in our coverage of technology.
There is a practical lesson in all of this for readers deciding what to do today. Start with the verified facts, be wary of anyone promising certainty, and prefer reversible steps while the evidence is still developing. Circumstances differ by country, income and personal situation, so general guidance should always be weighed against your own context before you act on it in any significant or lasting way.