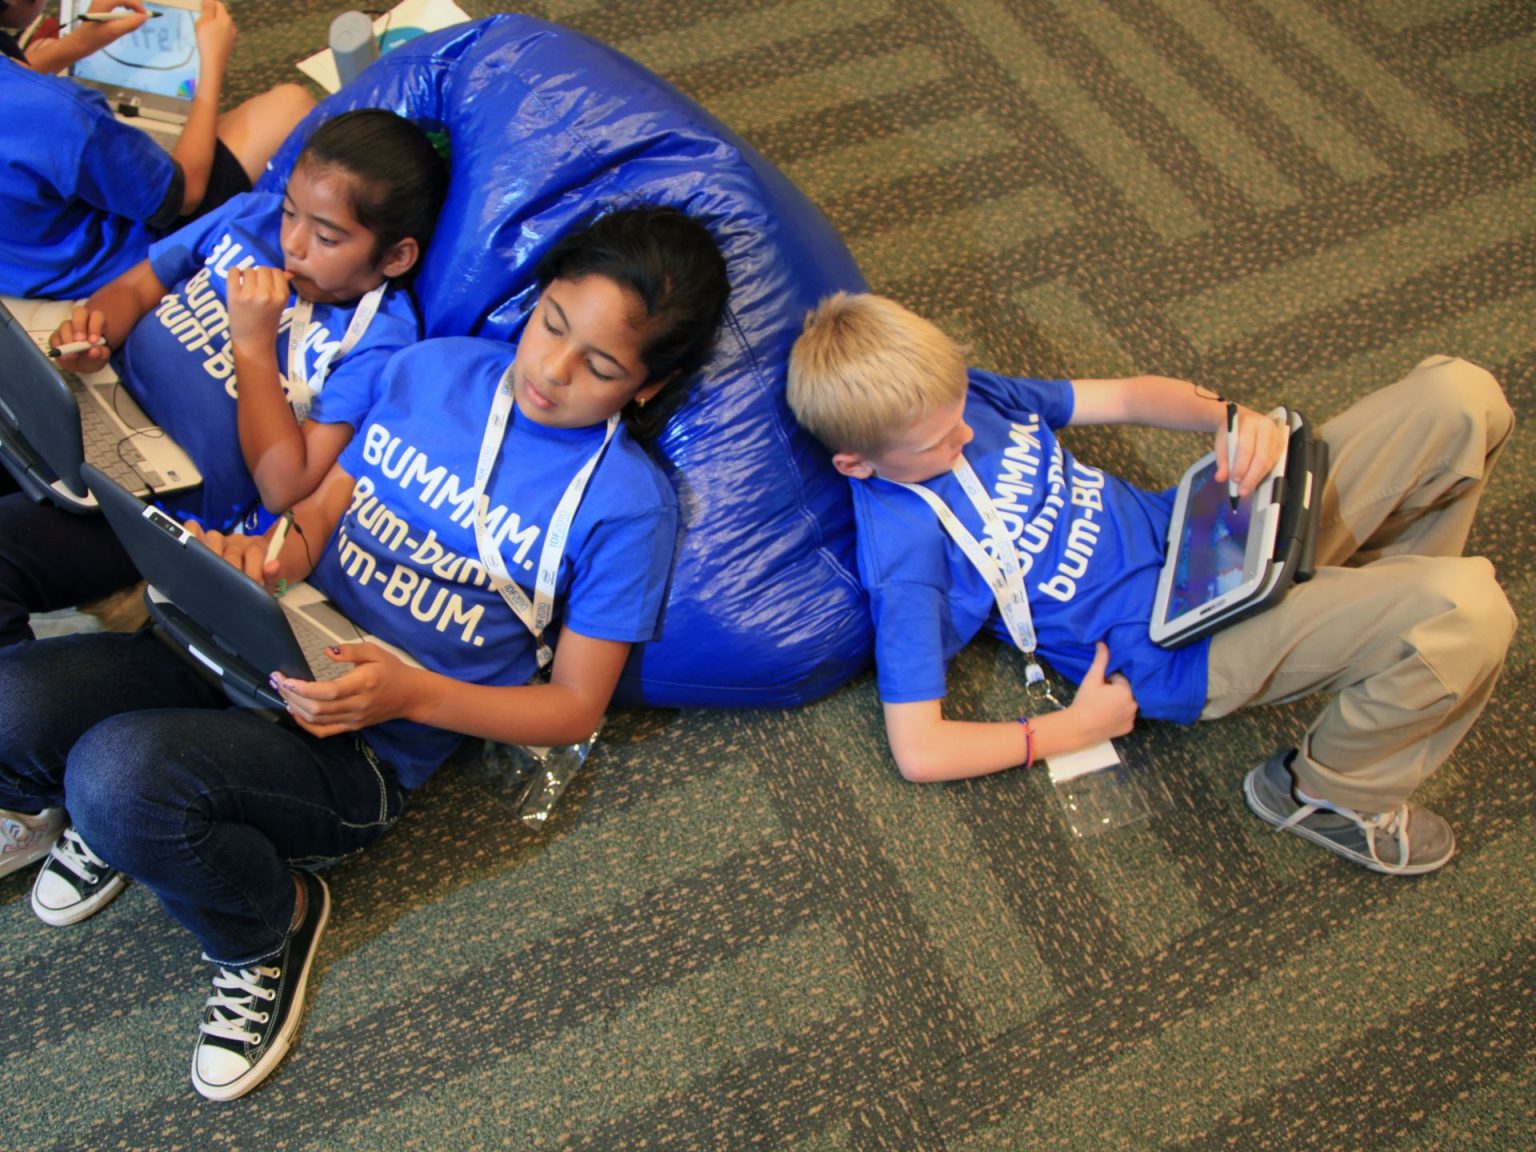

A child’s first data trail now begins before their first day of school. Photos shared by proud parents, educational apps in the classroom, games that profile behaviour, toys that listen — the average young person accumulates thousands of data points held by companies they have never heard of. For years this happened in a regulatory gap: privacy law written for adults, applied loosely to the people least able to consent. That gap is now closing, and fast.
Britain’s age-appropriate design code, European digital rules and new American state laws share a philosophy: services likely to be used by children must be designed for children — private by default, minimal in data collection, and barred from nudging young users toward choices that serve advertisers. Platforms have begun redesigning in response, sometimes worldwide, because building one compliant product is cheaper than building five.
Our reporting on this shift focuses on what actually changes for families, because the distance between a law’s announcement and a child’s Tuesday evening can be considerable.
What the New Rules Actually Require
The core duties are concrete. Default accounts for minors must be private, with location tracking and behavioural profiling off unless justified. Data collected for one purpose — delivering a lesson, say — cannot quietly be repurposed for advertising. The UK regulator’s guidance at the Information Commissioner’s Office sets out the design standards in detail, and enforcement has moved from guidance to fines and forced changes at major platforms.
Age assurance is the contested frontier: checking that users are the age they claim, without building identity databases of children in the process. Privacy-preserving methods — estimation from behaviour or device-level signals — are advancing, but every approach trades accuracy against intrusion. Our technology coverage follows these cases because they will define how the whole internet, adults included, verifies itself in future.
The Design Question: Addictive by Default
Regulators have moved beyond data into design itself. Infinite scroll, streaks, autoplay and recommendation tuned purely for engagement are increasingly treated as harms when aimed at children, not merely as product choices. The shift matters because it relocates responsibility: instead of parents policing every minute, the duty falls on the companies engineering the minutes. Safety campaigners reporting to the BBC’s technology desk describe the change as the end of the ‘parental blame’ era of online safety.
Platforms respond in layers — teen accounts with default limits, parental dashboards, restricted messaging from strangers. Some changes are substantive; others are theatre, and the regulators’ new audit powers exist to tell the difference. Parents should treat built-in tools as a floor, not a finish line: they work best alongside the unglamorous basics of shared passwords for young children, charged devices outside bedrooms, and conversations that start before problems do.
What Families Can Do This Week
Practical steps have unusual leverage right now, because platform defaults are in flux. Review the privacy settings of the apps your children actually use; turn off ad personalisation and location history; check what the school-issued tools collect, which parents have a right to know. For younger children, co-use beats surveillance — watching together occasionally teaches more than any monitoring app, and keeps the channel open for the day something goes wrong.
The deeper point is generational. Today’s children will be the first adults whose entire lives are documented in commercial databases assembled before they could spell ‘consent’. The rules now being written decide whether that documentation becomes a resource they control or a profile that follows them. On the outcome of that argument — being fought in parliaments, courts and settings menus — a great deal of the future internet quietly depends.